ДЕКЛАРАЦИЯ ЗА ПОВЕРИТЕЛНОСТ
Application: "Disasters in Bulgaria (Bulgaria Disaster)"
Last update:Septemberr15, 2026 (GDPR Compliance Revision: September 2026)
Language: English Version
1. Introduction
This privacy policy describes how the application "Disasters in Bulgaria (Bulgaria Disaster)" collects, uses, processes, and protects the personal data and information of its users. The application fully complies with Regulation (EU) 2016/679 of the European Parliament and of the Council (General Data Protection Regulation - GDPR) and applicable Bulgarian legislation, including the Personal Data Protection Act (ZPLD).
2. Data Controller & Contact Information
The Data Controller responsible for processing personal data within the meaning of Article 4(7) GDPR is the developer of the "Disasters in Bulgaria" application:
📧 Contact Email:[email protected]
📍 Legal Status & Office:Online application without a physical customer service office. Inquiries regarding data protection and GDPR rights should be directed electronically to the contact email above.
🌐 Official Website:www.bulgariadisaster.ednabulgarka.com
3. Categories of Data Collected & Legal Bases for Processing (Art. 6 GDPR)
The application does not require user account registration and does not construct persistent commercial user profiles. Data processing is limited to specific functionalities designed for disaster awareness and public safety:
3.1. Data Entered by the User (SOS Points)
When submitting an SOS point, the user may at their own discretion voluntarily enter:
Name or pseudonym
Phone number
Description of the emergency situation
Photos / images (optional)
Geographic location of the event
These data points are entered voluntarily and published solely to inform other users of ongoing local hazards. They are never processed for direct marketing, commercial profiling, or user tracking outside the signal's scope.
| 📌 LEGAL BASIS: SOS POINTS & RESPONSIBILITY Legal Basis (Art. 6(1)(a) & Art. 6(1)(d) GDPR): Processing is based on explicit voluntary Consent granted upon submitting the signal, as well as the protection of Vital Interests of data subjects or other natural persons during emergency situations. User Responsibility: The user bears sole legal responsibility not to enter third-party personal data without a lawful legal basis. |
|---|
3.2. Location Data (Optional)
Location data is accessed only after explicit permission granted by the user via system dialogs. Location access is used exclusively to display current position on the emergency map and assist in adding point coordinates. Location data is never used for continuous background tracking or profiling.
| 📌 LEGAL BASIS: GEOLOCATION DATA Legal Basis (Art. 6(1)(a) GDPR): Processing is based strictly on the user's explicit Consent granted through device location permissions, which can be revoked at any time via device settings. |
|---|
3.3. User-Entered API Keys
The application allows users to optionally enter personal API keys to fetch enhanced data from third-party services: OpenWeatherMap, NASA FIRMS, Copernicus Emergency Management Service (CEMS), and EUMETSAT. API keys are stored exclusively locally on the user's device, are never transmitted to the developer's servers, and are not shared with third parties.
Legal Basis (Art. 6(1)(b) GDPR):Performance of requested app functionality at the user's request.
3.4. Technical and Diagnostic Data (Anonymized)
The application processes limited technical diagnostics such as device model, operating system version, and crash/error logs. This identifier is a random software UUID for the installation, not a personal or hardware device identifier (it is not an IMEI or MAC address). These telemetry logs are fully anonymized, do not allow direct identification of natural persons, and are used solely to ensure application stability and security.
Legal Basis (Art. 6(1)(f) GDPR):Legitimate interest of the Data Controller to maintain software stability, prevent cyber threats, and optimize application performance.
4. External Services & International Data Transfers (Art. 44-49 GDPR)
To deliver real-time emergency mapping and satellite telemetry, the application integrates with external service providers:
4.1. Google Firebase (Firestore, Cloud Storage, Authentication)
Used for real-time synchronization of hazard points and cloud database storage. Firebase processes technical metadata (IP address, device identifiers) and user-entered SOS data.
International Data Transfers:Data processing by Google LLC may involve data transfers outside the European Economic Area (EEA) to the USA. Such transfers are safeguarded under the EU-U.S. Data Privacy Framework (DPF) and European Commission approved Standard Contractual Clauses (SCCs). Google's privacy terms apply: https://policies.google.com/privacy
4.2. NASA FIRMS, CEMS, EFFIS, EUMETSAT, OpenStreetrMap, WeatherAPI.com and OpenWeatherMap
NASA FIRMS: Active wildfire observations (Public Domain). Requests process IP address and query parameters.
Copernicus EMS (CEMS): Satellite disaster monitoring (CC BY 4.0). Supports user API keys; processes request IP metadata.
EFFIS: European Forest Fire Information System (CC BY 4.0). Data fetching without API keys.
EUMETSAT: Satellite fire monitoring data (CC BY 4.0). Supports user API keys and processes query parameters.
OpenStreetrMap: Hidrants. (Open Database License)
OpenWeatherMap: Weather data: temperature, precipitation, wind.(Open Database License)
WeatherAPI.com:Weather data: temperature, precipitation, wind.(Attribution)
5. Purposes of Data Processing & Prohibitions
Personal and technical data are processed strictly for the following exhaustive purposes:
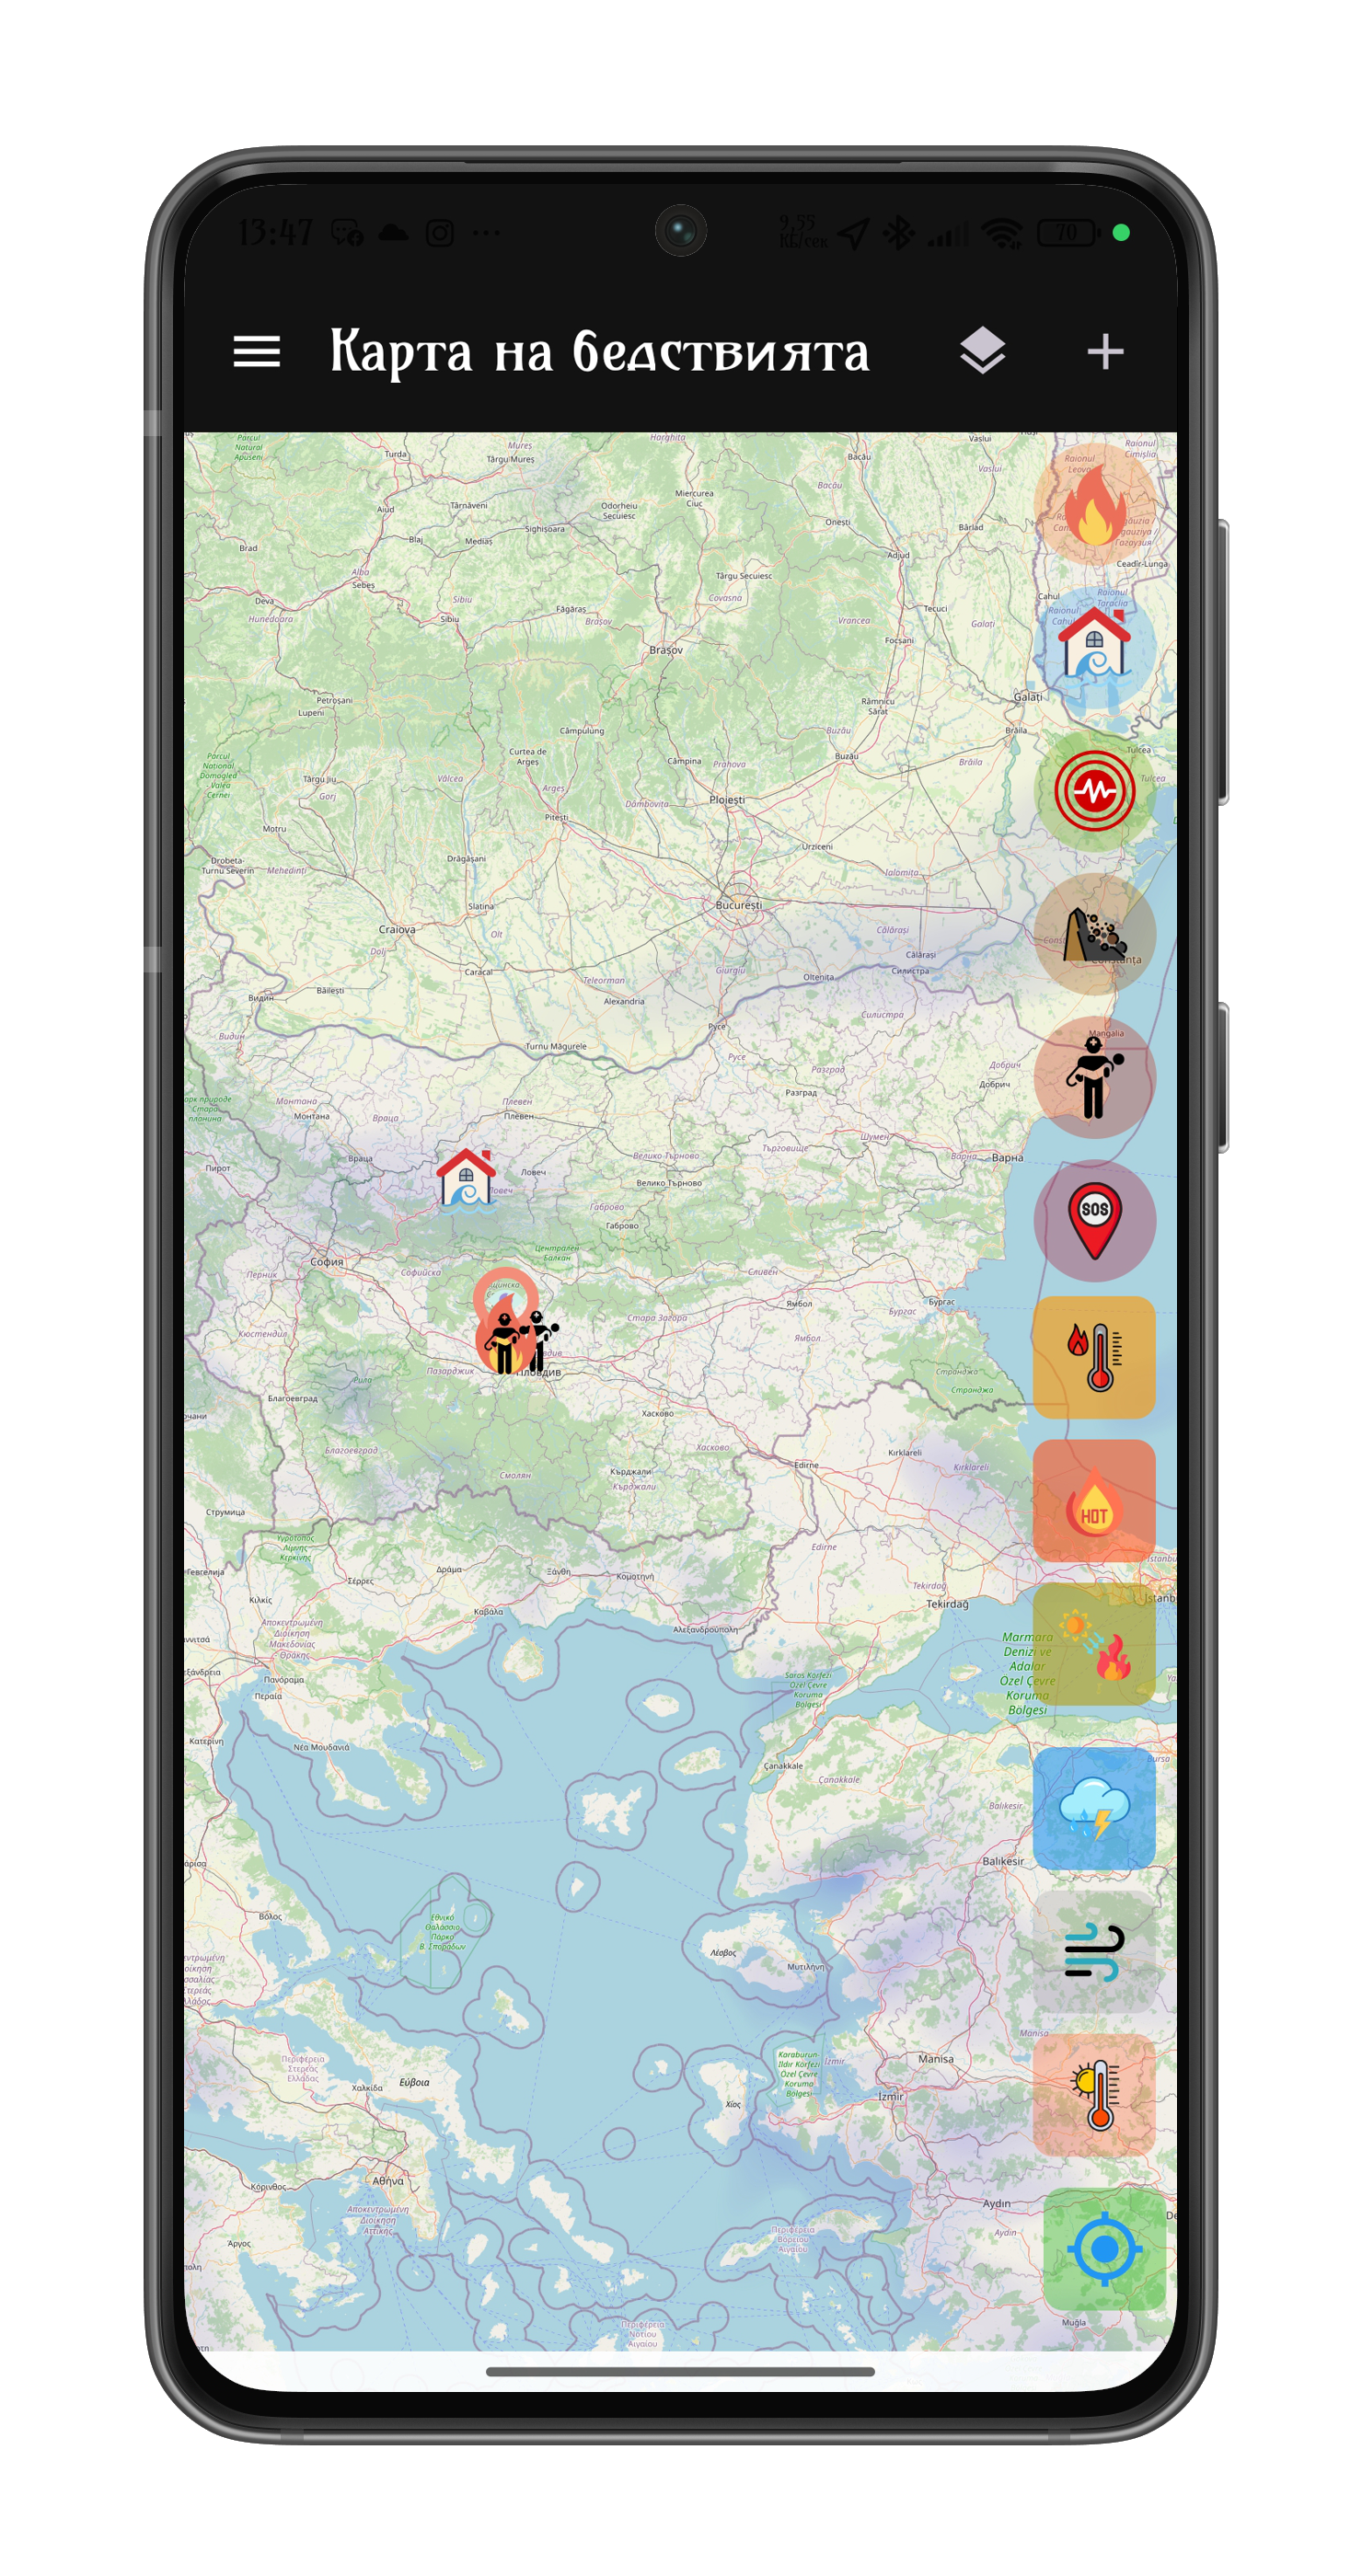
Visualizing real-time disaster zones, weather hazards, and user SOS markers on interactive maps.
Facilitating peer-to-peer awareness during natural emergencies.
Maintaining system security, operational integrity, and error diagnostics.
| 📌 STRICT DATA PROHIBITIONS • Data Commercialization: Personal data is NEVER sold, rented, or traded. • Advertising: The application contains NO third-party commercial advertisements. • Profiling & Automated Decisions: Data is NEVER processed for automated decision-making or behavioral profiling under Art. 22 GDPR. |
|---|
6. Data Storage, Security & Retention Periods (Art. 5(1)(e) & Art. 32 GDPR)
The Controller enforces technical and organizational measures to protect data against unauthorized access, loss, or alteration, including HTTPS/TLS encryption in transit and strict Firebase Security Rules.
6.1. Retention Periods
SOS Points & Emergency Signals:Stored in active cloud database for the duration of the emergency event, up to a maximum retention of 30 days following signal resolution, after which signals are permanently deleted or fully anonymized.
Technical & Diagnostic Logs:Crash logs and server metadata are retained for up to 90 days strictly for stability diagnostics before automatic purging.
API Keys:Stored exclusively in local device storage (SharedPreferences) and deleted immediately upon app uninstallation or manual cache clearance by the user.
7. Your Rights Under GDPR & Procedure for Exercising Rights
Under Articles 15 to 22 of the GDPR, users have the following statutory rights regarding their personal data:
Right of Access (Art. 15):Right to request confirmation and a copy of personal data processed.
Right to Rectification (Art. 16):Right to request correction of inaccurate personal data.
Right to Erasure / 'Right to be Forgotten' (Art. 17):Right to request deletion of voluntary SOS signal data.
Right to Restriction of Processing (Art. 18):Right to request limitation of data processing under legal conditions.
Right to Withdraw Consent (Art. 7(3)):Right to withdraw location permissions or consent for SOS signal data at any time without affecting prior lawful processing.
Right to Object (Art. 21):Right to object to processing based on legitimate interests.
7.1. Procedure and Timelines for Exercising Rights (Art. 12 GDPR)
To exercise any of the rights listed above, please submit a written request via email to: [email protected]
The Controller will verify your identity (if applicable) and respond to your request free of charge without undue delay and at the latest within ONE MONTH (30 days) of receipt, as mandated by Article 12(3) GDPR. If the request is complex, this period may be extended by two further months with prior notice.
7.2. Right to Lodge a Complaint with a Supervisory Authority
If you consider that the processing of your personal data infringes GDPR provisions, you have the right to lodge a formal complaint with the Bulgarian lead supervisory authority:
Commission for Personal Data Protection (CPDP / КЗЛД)
📍 Address: 2 Prof. Tsvetan Lazarov Blvd., Sofia 1592, Bulgaria
📧 Email: [email protected] | 🌐 Website: www.cpdp.bg
8. Cookies and Storage Technologies
The application does not use HTTP cookies or tracking web beacons. Local device storage (SharedPreferences / KeyStore) is used solely for saving operational preferences and API keys locally. External third-party services operate under their respective privacy policies.
9. Changes to this Privacy Policy
This Privacy Policy may be updated periodically to reflect application enhancements or evolving statutory requirements. All revisions will be published within the application and on the official website prior to taking effect.
10. Contacts & Legal Disclaimer
For any questions regarding this policy or data protection compliance, contact:
📧 Email: [email protected]
🌐 Website: www.bulgariadisaster.ednabulgarka.com
| 📌 PUBLIC INTEREST & GOVERNMENT DISCLAIMER IMPORTANT PUBLIC DISCLAIMER: The application is of a purely informational and public-benefit nature. THE APPLICATION DOES NOT REPRESENT A GOVERNMENT ORGANIZATION OR OFFICIAL STATE ENTITY. Data displayed from emergency APIs or user SOS points does not constitute official state alerts and does not replace emergency response services (such as Emergency Number 112). Data may experience technical delays or inaccuracies and must not be solely relied upon for life-critical decisions without verification from official authorities. |
|---|